
For IAM leads replacing SAP IDM

Replacing SAP Identity Management.
Step by step, alongside your current setup.

SAP ends mainstream maintenance for SAP Identity Management 8.0 at the end of 2027. This page sets out the options you are being offered and how Nova IAM approaches the replacement: connect SAP via RFC/BAPI, reconcile the actual state, test for 90 days alongside SAP IDM.

30 minutes live on the demo system, with your questions.

End of mainstream maintenance
31 Dec 2027
Extended maintenance
until 2030
Pilot with Nova
90 days in parallel
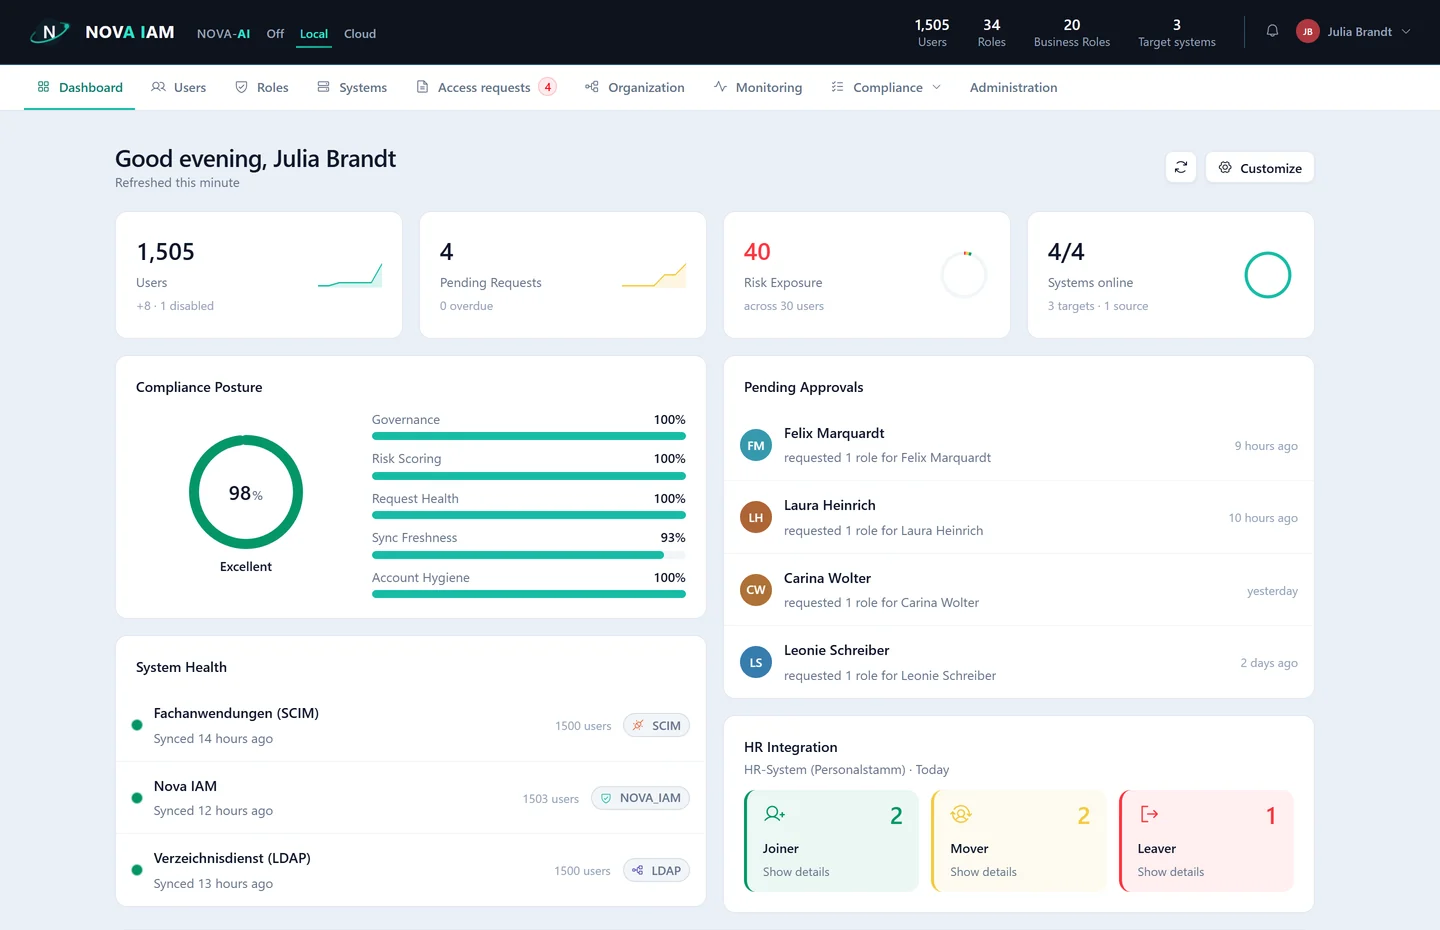
Nova dashboard with figures for users, requests, risk and target systems, plus compliance status, approvals, system health and HR integration
Nova dashboard · demo tenant with fictitious dataFull-size image →

Background

What SAP has announced

SAP Identity Management 8.0 runs on SAP NetWeaver Application Server Java, so SAP aligned its maintenance with SAP NetWeaver 7.5. In February 2024, SAP confirmed the end of maintenance and described extended maintenance as time to prepare and carry out a well-considered migration.

  1. 27 Apr 2020Maintenance to end of 2027

    SAP aligns maintenance of SAP IDM 8.0 with SAP NetWeaver 7.5.

  2. 6 Feb 2024End of maintenance confirmed

    SAP names 2027 and extended maintenance until 2030, and announces guidance for Entra ID with Microsoft.

  3. 26 Jun 2024First guidance

    SAP reports Microsoft’s first migration guide and works with DSAG on best practices.

  4. 4 Oct 2026As of this page

    Research date for all statements here.

  5. 31 Dec 2027End of mainstream maintenance

    for SAP Identity Management 8.0.

  6. 2030End of extended maintenance

    The last maintenance phase SAP names for SAP IDM.

For planning: a 90-day pilot, followed by migration support for which we plan around 12 weeks; the actual duration depends on the complexity of your SAP IDM setup. Selection and procurement come on top.

Sources: SAP, 27 Apr 2020, SAP, 6 Feb 2024, SAP, 26 Jun 2024 (SAP Community, posts by SAP); Microsoft Tech Community, 15 Feb 2024. Research as of 4 Oct 2026.

Options

Three options you are being offered right now

Each of the three has good reasons behind it. Which one fits depends on your landscape. Statements about SAP and Microsoft are based on their published material; the assessment of IGA suites is our own.

Keep running SAP IDM

Obvious because …
the system works, the processes are established and SAP offers extended maintenance until 2030.
Difficult because …
it only postpones the replacement: SAP describes extended maintenance as time for a well-planned migration, and SAP offers no other on-premise identity management product.
Still a fit if …
your target system is decided and you use the time until 2030 for a careful, staged migration, for example alongside your move to S/4HANA.

Source: SAP, 6 Feb 2024, including the SAP author’s reply of 23 Feb 2024 in the comments
Microsoft Entra ID with SAP Cloud Identity Services

Obvious because …
SAP has prepared this path with Microsoft: according to Microsoft, SAP recommends Entra ID for the migration, both vendors publish guidance, and SAP Cloud Identity Services are the centre of SAP’s IAM strategy.
Difficult because …
the target architecture consists of several cloud services: Entra ID provisions to SAP S/4HANA via SAP Cloud Identity Services, automated role assignments require a Microsoft Entra ID Governance licence, and fine-grained SoD checks are added through SAP Cloud Identity Access Governance or a GRC product.
Still a fit if …
Entra ID is already your leading directory, your SAP landscape is moving to the cloud and you can approve cloud services for identity data.

Sources: Microsoft, 15 Feb 2024, Microsoft Learn migration guide (retrieved 4 Oct 2026), SAP, 26 Jun 2024

A large IGA suite

Obvious because …
suites cover many systems and governance functions beyond SAP, and several vendors address the end of SAP IDM maintenance, some with dedicated migration packages.
Difficult because …
the scope usually goes beyond your current SAP IDM scenarios. Licence metrics, operating model (SaaS or on-premise) and implementation effort differ by vendor and belong in the evaluation early on.
Still a fit if …
your landscape extends well beyond SAP and Microsoft and you want to connect many non-SAP systems with ready-made connectors.

Examples: Omada, SAP IDM migration, Saviynt for SAP (retrieved 4 Oct 2026)

And where does Nova IAM fit?

Nova fits if …
SAP ERP or S/4HANA and SAP HCM are at the centre of your landscape, Nova is to run in your own infrastructure and you want to test the replacement alongside your current setup.
Nova is not a fit if …
you are looking for a replacement for your corporate IdP, a password vault with session recording or customer logins (CIAM). The roadmap lists these under “What Nova does not want to be”.

Approach with Nova

How Nova approaches the replacement

There is no automatic one-to-one migration; SAP also describes the move as reviewing and adapting the landscape, workflows and configuration. Nova therefore starts from the actual state of your systems.

  1. Connect

    SAP ERP and S/4HANA via RFC using the SAP NetWeaver RFC SDK, accounts and roles via BAPIs, with no agent in the SAP system. SAP HCM supplies the organisation via RFC and personnel master data via a virtual directory server (LDAP) or a staging table. Nova also connects Active Directory, LDAP directories, Entra ID, SCIM and Keycloak.

  2. Reconcile

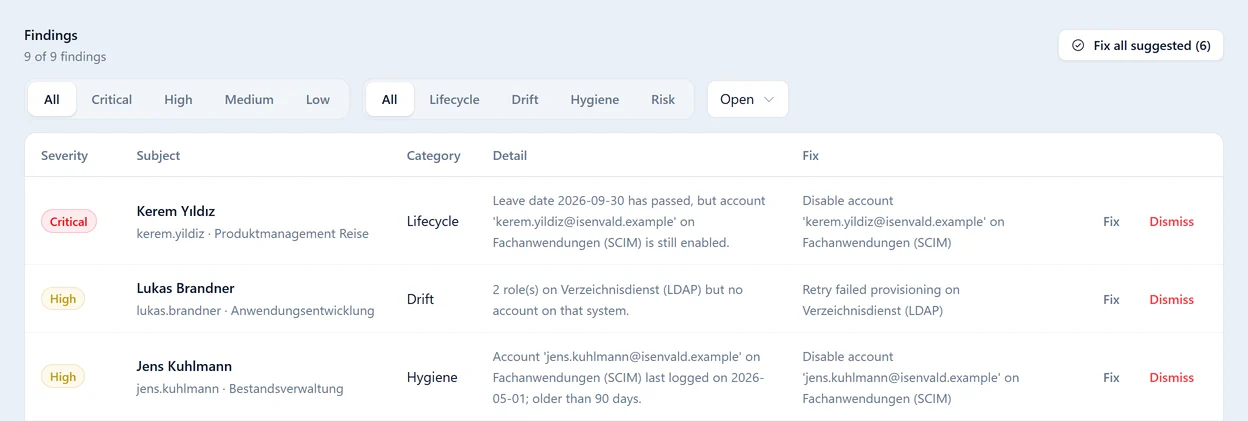
    Nova reads the actual role assignments back from SAP, including the children of composite roles, and reconciles Nova, SAP and LDAP/AD three ways. The healthcheck runs 19 checks per user in four groups, 11 of them with a suggested fix.

  3. Adopt the role model

    Nova imports the SAP role catalogue with German and English role texts. Backend roles Nova does not yet know are adopted or discarded with one click. Time limits go straight into the SAP role assignment as FROM_DAT/TO_DAT.

  4. Run in parallel and decide

    In the 90-day pilot, Nova runs alongside SAP IDM, which stays in operation. You test requests with SoD checks, recertification and the audit log against your systems, measured by success criteria from week 1.

Nova healthcheck findings list: findings on individual accounts and identities, each with severity, category, detail and suggested fix
Healthcheck findings with severity, detail and fix · demo tenant with fictitious dataFull-size image →

For SAP Basis and architecture

Typical SAP IDM tasks and their status in Nova

What is included as standard today, what is connected in the project and what is still missing, at a glance.

Status according to the integration directory and the roadmap, as of 4 Oct 2026, release 2026.08.2.
TaskIn NovaStatus
Manage accounts and roles in SAP ERP and S/4HANA (on-premise)SAP connector via RFC/BAPI, roles with validity datesStandard
Take over personnel and organisational data from SAP HCMSAP HCM as the leading HR source: org structure via RFC from HRP1000/HRP1001, read-only; personnel master data via a virtual directory (LDAP) or a staging tableStandard
Active Directory and LDAP directoriesActive Directory and LDAP via LDAPv3Standard
Microsoft Entra IDEntra ID via Graph APIStandard
Cloud applications via SCIMSCIM 2.0, genericStandard
SAP BTP and SAP Cloud Identity ServicesSCIM via Cloud Identity Services, WebSocket RFC being trialledBeta
SAP SuccessFactors as HR sourceIntegration in the project via ODataProject integration
SAP S/4HANA CloudConnector on the roadmapPlanned
Requests and multi-level approvalsSelf-service requests, workflows with stages and approvers, delegation rulesStandard
SoD check before approvalSoD conflicts visible in the request before the decisionStandard
RecertificationCampaigns with one decision per assignmentStandard
Evidence for internal and external auditAudit log with actor, time and origin, export as CSV or JSONStandard
SAP risk analysis via SAP Cloud Identity Access GovernanceIAG connector, scheduled for Q4 2026 in the roadmapPlanned
Replacing the corporate IdPNova does not replace your IdP; an optional plugin makes Nova an OIDC provider for internal applicationsNot intended

Timeline

How the replacement runs with Nova

From the first meeting to switching off SAP IDM. Terms for the pilot and maintenance are on the pricing page.

  1. Beforehand

    Demo and analysis

    30 minutes live on the demo system, followed by an initial analysis of your SAP IDM scenarios.

  2. Week 1

    Success criteria

    3–5 measurable criteria, defined jointly.

  3. Up to day 90

    Parallel operation

    Connect Nova to your systems, reconcile the actual state, adopt the role model. SAP IDM stays in operation.

  4. Day 90

    Decision

    Cutover, extension or withdrawal.

  5. Then, planned at around 12 weeks

    Migration

    Migration support in the Maintenance & Consulting package: data migration and initial reconciliation, admin training and run-book handover; after that you can switch SAP IDM off.

For your decision paper

Five sentences to pass on

Each sentence is backed up on this page or the pages it links to.

  1. SAP ends mainstream maintenance of SAP Identity Management 8.0 at the end of 2027; SAP offers extended maintenance until 2030.
  2. Nova IAM is a self-hosted identity governance platform; it connects SAP via RFC/BAPI, plus Active Directory, Entra ID, SCIM and Keycloak.
  3. We test Nova for 90 days alongside SAP IDM, with success criteria defined in advance, and then decide on cutover, extension or withdrawal.
  4. Maintenance is an annual fee by size class, with no per-user or per-system charges.
  5. AI features are optional and off by default; the assistant has no rights of its own, and changes made via the AI chat are logged with their origin.

FAQ on replacing SAP IDM

How long will SAP Identity Management be maintained?

Mainstream maintenance for SAP Identity Management 8.0 ends at the end of 2027, on 31 December 2027. After that, SAP offers extended maintenance until 2030 and describes it as time to plan and carry out a well-considered migration. Research as of 4 October 2026.

Which successor does SAP recommend?

According to Microsoft, SAP recommends Microsoft Entra ID as the service for the migration; both vendors are producing migration guidance for it. SAP Cloud Identity Services are the centre of SAP’s IAM strategy.

Can the SAP IDM configuration be migrated automatically?

Not one to one. SAP also describes the move as reviewing and adapting the landscape, workflows and configuration. Nova reads the role catalogue and the actual role assignments directly from SAP and reconciles them against the target state; you configure approval workflows anew in the editor.

Does SAP IDM have to be switched off for the pilot?

No. The pilot runs for 90 days alongside your existing tool, which stays in operation. In week 1 we jointly define 3–5 success criteria; after 90 days you decide on cutover, extension or withdrawal.

How does Nova connect to SAP?

Via RFC using the SAP NetWeaver RFC SDK with a technical SAP user, without an agent or intermediate layer in the SAP system. Nova writes accounts and roles through BAPIs and checks every write against the BAPI return. Nova reads the organisational structure from SAP HCM via RFC, read-only.

Where does Nova run?

In your infrastructure, on-premise or in your private cloud: one Python process and one PostgreSQL database, delivered as containers.

Further reading

Ask your questions live on the system.

30 minutes on the demo system: SAP integration, reconciliation and the request process in the demo tenant, geared to your SAP IDM scenarios.

What happens next

  1. ReplyWe usually get back to you on the same working day and agree a date with you.
  2. PreparationWe prepare the demo around the topics you name.
  3. 30 minutes via video callLive on the demo system with fictitious data: you ask, we show the relevant views.